Email
iCloud Mail Needs a Redesign: A Webmail Concept
Apple’s hardware is world-class, but iCloud Mail on the web feels abandoned. Here is what iCloud Mail offers today, why it needs a rebuild, and a concept UI I mocked up.
From Nigerian prince emails to modern phishing, 419 scams evolved with the internet, and they expose how email’s openness can be exploited.
 Paul O'Brien
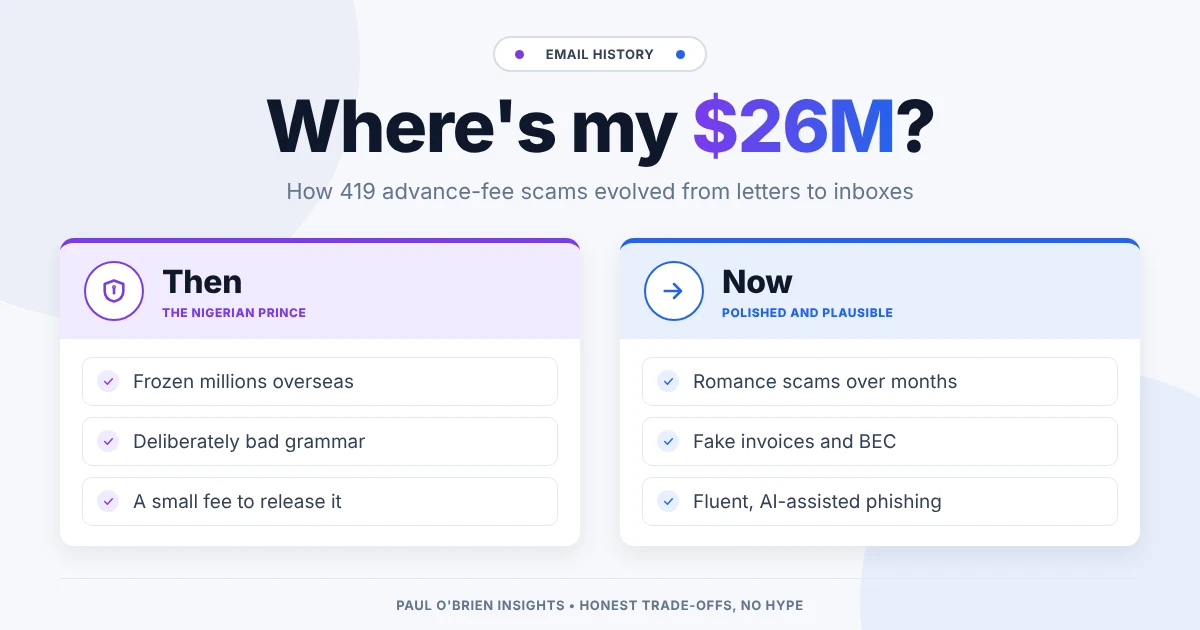
At least, that’s what the email promised. If you were online in the early 2000s, it probably found you too. The message was long and dramatic, full of political instability, frozen accounts, dying relatives and vast sums of money trapped overseas.
At first there was no demand, just a story and an appeal for help. Only after some back-and-forth would a small “administrative fee” appear, positioned as the final obstacle between you and sudden wealth. It was implausible, badly written and oddly theatrical, and “Nigerian prince” became shorthand for something obviously fraudulent. These became known as 419 scams. This post covers where the name comes from, why the bad grammar was deliberate, and what the same trick looks like in your inbox today.
Short answer: a 419 scam is advance-fee fraud: you are promised a large reward and asked to pay something up front to release it. The name comes from Section 419 of the Nigerian Criminal Code. The theatrical “prince” emails have largely given way to romance scams, business email compromise and polished phishing, but the mechanics are the same, and they work because email lets anyone reach anyone.
| Era | Channel | What it looked like |
|---|---|---|
| 18th and 19th centuries | Letters | The “Spanish Prisoner”: help free a wealthy captive and share the fortune |
| Late 1970s and 1980s | Post, then fax and telex | Letters from supposed officials or executives sitting on frozen government funds |
| Late 1990s and 2000s | The “Nigerian prince” and oil minister, sent in vast volumes | |
| Today | Email, messaging, social media, dating apps | Romance scams, business email compromise, fake invoices and phishing |
The term comes from Section 419 of the Nigerian Criminal Code, part of the chapter on obtaining property by false pretences. It covers schemes where someone is persuaded to hand over money or property on the strength of a lie, typically the promise of a much larger return that never materialises.
Many of the early email versions came from criminal networks operating in Nigeria, but the technique itself is not geographically unique. Advance-fee fraud existed long before email: the Spanish Prisoner letters ran on the same idea centuries earlier. Today it is carried out from many different countries using a wide range of digital channels.
The core structure is simple:
In legal terms, it is fraud. In practical terms, it is psychological manipulation stretched over time. The “Nigerian prince” emails were only the digital expression of a much older crime: convince someone a windfall is close, then introduce just enough friction to require payment.
For years, people assumed the spelling mistakes and awkward phrasing were signs of incompetence. In reality, the rough edges served a purpose.
Advance-fee fraud operates at scale. These emails reached thousands, sometimes millions, of inboxes at once. Sending them cost almost nothing. Following up with each person who replied took time and effort. At that volume, efficiency matters more than persuasion.
Poor grammar and implausible stories acted as a filter. They discouraged sceptical readers and attracted those more willing to continue the exchange, often people under financial pressure, isolated, grieving or simply having a moment of optimism. Fraud does not select for education; it exploits circumstance and psychology.
This is not just my reading. In a 2012 Microsoft Research paper titled Why do Nigerian Scammers Say They are from Nigeria?, Cormac Herley argued exactly this: the opening email works as the scammer’s filter. Because so few recipients are ever going to pay, a believable message would attract too many replies from people who would drop out later, and every one of those costs the scammer time. An outlandish story makes the most gullible select themselves.
What looked careless was strategic. The early 419 emails were already optimised, not for universal appeal, but for operational efficiency.
They also revealed something fundamental about how email works. The system was designed to be open. Anyone, anywhere, could send a message to anyone else, and the protocol did not verify identity in a way that guaranteed authenticity. A sender could invent a name, adopt a title or perform authority, and the message would still arrive. That openness is the reason email became universal. It is also the reason deception travels through it so easily.
As the emails spread, a small counter-culture emerged. Some recipients responded playfully, dragging conversations out to waste scammers’ time. Sites like 419Eater documented elaborate efforts to turn the tables, often very funnily. It was easy to focus on the absurdity.
But not everyone treated it as a joke. Advance-fee fraud has caused serious financial and emotional harm. Some victims lost savings or borrowed heavily believing a transfer was imminent. In rarer cases people travelled abroad to “complete” the transaction and found themselves in danger. What began as an implausible email sometimes escalated into coercion or threat.
The humour masked the seriousness of what was, and still is, an organised criminal model exploiting the thing email makes possible: direct, unfiltered access to strangers across borders.
Do those emails still exist? Yes, but rarely in the form we remember.
The early 419 format has largely given way to more sophisticated approaches. Romance scams unfold over weeks or months, building emotional trust before introducing financial pressure. Business email compromise (BEC) schemes mimic internal company communication and rely on timing and plausibility rather than fantasy. Phishing emails copy familiar login pages with unsettling precision.
The money involved is not small. The FBI’s Internet Crime Complaint Center put reported BEC losses in the US at about $3 billion for 2025, the second-largest loss category after investment fraud. Those are only the cases people reported.
The tone has changed. The mechanics have not. Where early 419 emails relied on exaggeration and spectacle, modern scams rely on realism. The spelling errors that once filtered for the credulous have been replaced by fluent prose, often helped by automation and AI tools. The linguistic barrier that once exposed fraud has narrowed considerably. Awareness has grown, but so has professionalism. I cover the wider picture in why spam isn’t disappearing.
Email remains open, global and largely permissionless. Trust is layered on top of a neutral transport system. Standards such as SPF, DKIM and DMARC help, but they prove which domain a message came from, not whether the person behind it is honest. A scammer with their own properly configured domain passes those checks. It is worth knowing which “From” address you can actually trust.
That design decision is why email became indispensable. It lets businesses operate, governments communicate, families stay in touch and ideas travel freely. It also lets deception travel just as easily.
The Nigerian prince emails did not expose a flaw that was later fixed. They exposed a trade-off built into the medium from the beginning. Security in email has never lived solely in encryption or filters. It has depended heavily on human behaviour: on scepticism, verification and, perhaps most importantly, pause.
“If it sounds too good to be true” became common advice for a reason. These scams rely on urgency and information imbalance. One side appears to hold all the opportunity; the other is asked to act quickly with limited context. An unexpected opportunity. A looming deadline. A request that feels small and harmless in isolation. Click here. Reply quickly. Keep this confidential.
Email’s strength is that it is asynchronous. It creates space between receiving and responding, and that space allows for reflection, cross-checking and second thoughts. Used deliberately, the gap becomes protective. In practice, that means:
The Nigerian oil minister may have faded from our inboxes, but the dynamic he represented has not disappeared. It has adapted alongside the medium. Email keeps working because it is open and flexible, and that same openness means trust will always need to be supplied by the people using it.
We laughed at the promise of $26 million. What those emails really demonstrated was something more enduring: openness comes with a cost.
It refers to Section 419 of the Nigerian Criminal Code, which deals with obtaining property by false pretences, the offence behind advance-fee fraud.
Partly by design. An implausible message filters out sceptical readers, so the scammer only spends time on people likely to pay. Cormac Herley’s 2012 Microsoft Research paper set out this argument.
Yes, but they are a small part of the picture. The same advance-fee mechanics now turn up in romance scams, fake invoices and business email compromise.
They help stop people spoofing domains they do not control. They do not stop a scammer sending from their own domain, so the content still needs a sceptical read.
Note: checked and updated 17 October 2026. Sources: Wikipedia: advance-fee scam, The Register on Herley’s Microsoft Research paper, CyberScoop on the FBI IC3 2025 report, NCSC: report a scam email.
Get the next post by email. Free, no ads, and you can leave any time.
Apple’s hardware is world-class, but iCloud Mail on the web feels abandoned. Here is what iCloud Mail offers today, why it needs a rebuild, and a concept UI I mocked up.
A technical look at paid Outlook and Exchange Online: which security features need which plan, how it compares to Google Workspace and Fastmail, and who should pick each.
AI is creeping into every email client. Here is how to switch off Gemini, Copilot and Apple Intelligence in Gmail, Outlook and Apple Mail, what you lose, and why I think email works fine without it.
Comments